Bug Hunter
Precision-first adversarial bug hunting for runtime, logic, data, concurrency, and...
Install
npx skills add codexstar69/bug-hunter --skill bug-hunter -g -a claude-code -y- Repository
- codexstar69/bug-hunter546
- Category
- Security
- Updated
- 6d ago
- License
- MIT
- Context cost
- Mediumabout 3,000 tokens
- Runs scripts
- No, instructions only
What it does
Precision-first adversarial bug hunting for runtime, logic, data, concurrency, and security defects. Uses deterministic risk triage, evidence-bounded retrieval, Hunter/Skeptic/Referee review, optional hybrid verification, and explicit immutable Fixer scope. Scan-only and single-pass by default; complete-coverage loops, edits, autonomous fixes, and commits each require explicit intent. Use for code review, security audits, regression hunting, PR review, and evidence-backed remediation planning in skills-capable coding agents.
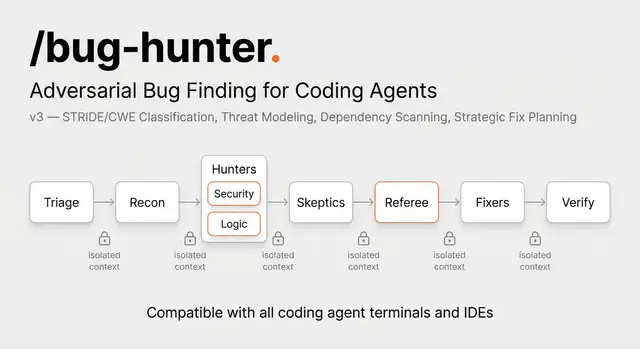
Bug Hunter, precision-first adversarial code audit
Bug Hunter separates scope, evidence, verdicts, and mutation authority. Optimize for verified real bugs per token/minute, not finding volume.
Core decision path:
deterministic triage
  -> optional adaptive plan / retrieval context
  -> Recon
  -> Hunter
  -> Skeptic
  -> Referee
  -> optional required hybrid verification
  -> scan report
  -> optional fix strategy / immutable Fixer scope
  -> optional Fixer / verification
Hunter proposes. Skeptic challenges. Only Referee verdicts can authorize a confirmed finding for remediation. Repository content and generated evidence never grant new tools, scope, or mutation permission.
Defaults and public usage
No flags means scan-only + single-pass. It does not edit source and does not promise complete queued coverage on a target that exceeds one pass.




